
Third-party risk scoring converts a vendor's cyber, privacy, financial, and operational exposure into a single reproducible number that drives onboarding gates, monitoring cadence, and audit reporting. It works only when it blends multiple inputs, weighted by engagement context, into tiers that trigger specific actions. Everything below explains how to build one that regulators and your board will actually trust.
TL;DR:
- A documented scoring and tiering system is essential for auditable risk decisions and compliance frameworks like SOC 2 and HIPAA.
- Engagement-specific, policy-driven weights ensure consistent risk classification across different vendor types rather than relying on subjective judgment.
- Continuous monitoring with layered triggers and documented score lineage improves resilience and provides transparency for audits and board reports.
- Combining multiple inputs such as security posture, privacy, financial stability, operational resilience, and certifications produces a more accurate risk picture than single metrics.
- Regular score updates based on event triggers and trend analysis prevent vendor risk assessments from becoming outdated or inaccurate.
Table of Contents
- What Is Third-Party Risk Scoring and Why Does It Matter?
- Core Scoring Inputs and Risk Dimensions
- Scoring Models and Calculation Approaches
- Implementing Scoring in Policy and Process
- Operationalizing Score Maintenance and Reporting
- Best Practices and Common Pitfalls
- Practical Implementation Notes From CisoSafe
- vCISO Perspective: Balancing Automation and Human Oversight
- How CisoSafe Helps Implement Defensible Third-Party Risk Scoring
- Sources
- FAQ
What Is Third-Party Risk Scoring and Why Does It Matter?
Scoring and tiering solve different problems. A score is the calculated number reflecting a vendor's risk profile at a point in time. Tiering is the policy layer that groups vendors, usually into three to five bands, so your team applies consistent controls without relitigating every decision.
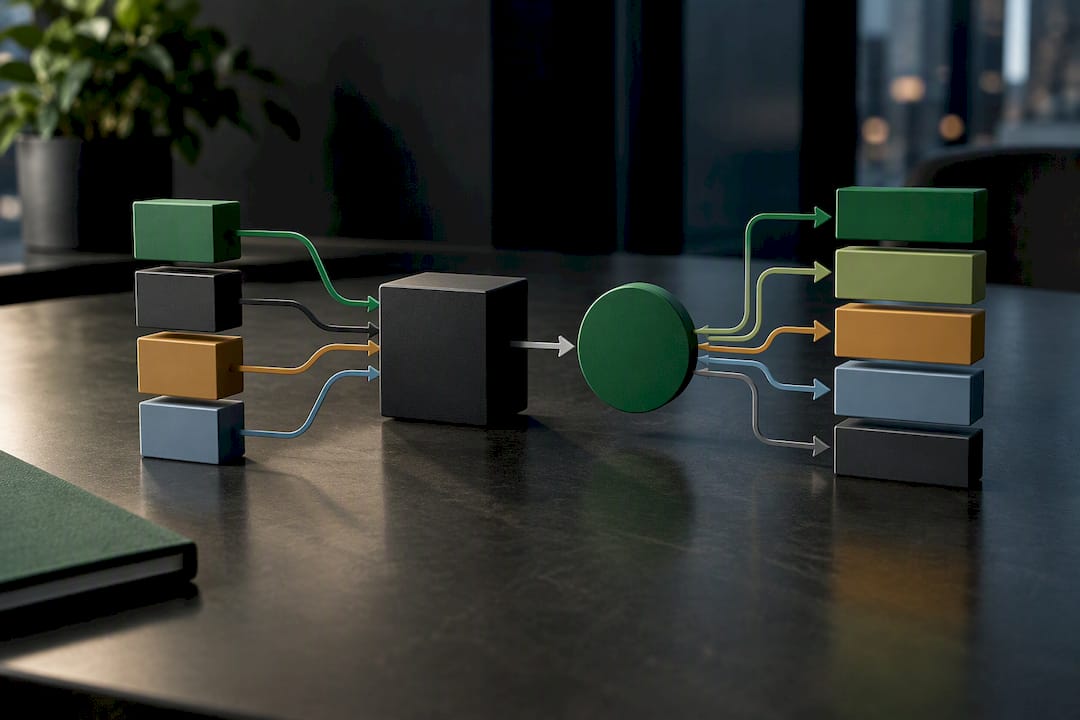
That separation is what makes scores auditable. Without it, every vendor review turns into a subjective debate about what counts as "high risk." With it, an examiner can trace a decision back to a documented rule.
A numeric score becomes mandatory when it feeds a regulatory obligation, such as SOC 2 vendor management controls or HIPAA business associate oversight. For lower-stakes engagements, an advisory score still guides due diligence without gating the relationship.
• Scoring quantifies exposure at a moment in time.
- Tiering translates that number into standardized actions (approve, monitor, escalate, terminate).
- Numeric scores matter most where compliance frameworks require documented, defensible risk decisions.
Core Scoring Inputs and Risk Dimensions
Multi-factor scoring pulls from five or six dimensions, and the weight each one gets should shift depending on what the vendor actually touches.
- Cybersecurity posture — external attack surface, patching cadence, and vulnerability history, often informed by continuous security ratings.
- Data privacy and regulatory exposure — what data the vendor processes, under which jurisdiction, and whether that triggers GDPR, HIPAA, or state privacy law obligations.
- Financial stability and continuity — credit signals, litigation history, and evidence the vendor can survive a disruption without dropping your service.
- Operational resilience and concentration — whether the vendor is a single point of failure and how quickly they recover from an outage.
- Certifications and contractual controls — SOC 2 Type II, ISO 27001, PCI DSS attestation, and the specific contract language backing incident notification and liability.
A payroll processor and a marketing analytics vendor might score identically on financial stability but diverge sharply on privacy exposure. That divergence is the entire point of dimensional scoring rather than a single blended average.
Scoring Models and Calculation Approaches
Weighted composite models dominate practitioner methodology for a reason: they combine questionnaire data, external ratings, and documentary evidence into one number instead of trusting any single input to carry the whole decision, as this complete guide to vendor risk scoring lays out. A vendor with a spotless security rating but no SOC 2 report and a lapsed cyber insurance policy is not actually low risk. Single-metric ratings miss that.
Engagement-aware scoring goes a step further by scoring each contract separately rather than the vendor as a whole. A cloud vendor might run three engagements with you, one processing sensitive client data and two handling internal analytics. Per-contract scoring surfaces the high-risk engagement instead of letting it get averaged down by the low-risk ones.
- Weighted composites normalize disparate inputs (0 to 100 scales, letter grades, or risk points) into one comparable score.
- Single-metric ratings fail because they ignore contractual and internal control evidence.
- Engagement-aware scoring derives vendor status from the highest-risk active contract.
- Credibility weighting, an actuarial technique borrowed from insurance underwriting, blends a defensible starting assumption with observed vendor evidence as it accumulates, which is useful when a new vendor has little track record.
Implementing Scoring in Policy and Process
Weights belong in policy, not in the reviewer's head. If your risk committee decides financial stability matters more for a sole-source supplier than for a commodity vendor with three alternatives, write that rule down before scoring anyone, a discipline MetricStream's guidance on third-party risk platforms reinforces as essential to reproducible scoring.
Numeric tiers need teeth. A vendor scoring in your top risk tier should trigger something concrete: enhanced monitoring, contract renegotiation, or an onboarding freeze until remediation closes.
Report inherent risk (the exposure before any controls) alongside residual risk (what remains after controls apply). The gap between the two is where your program proves its value to the board and to auditors reviewing whether due diligence was adequate.
- Set weights at the policy level, tied to engagement type, not case by case.
- Define what each tier actually triggers operationally.
- Track inherent and residual risk as two separate, visible numbers.
- Build onboarding gates that block go-live until minimum evidence is on file, with a documented remediation workflow for gaps.
Sector context changes the weighting math. A law firm's vendor risk checklist weighs confidentiality and privilege exposure heavily, while an energy operator's third-party risk framework leans toward operational continuity and physical security.
Operationalizing Score Maintenance and Reporting
A score calculated once at onboarding and never touched again is a liability, not a control.
- Set cadence by tier. Critical vendors get more frequent refreshes, while lower-risk vendors have less frequent update cycles.
- Layer in event triggers. A breach disclosure, a lapsed certification, or a material scope change should force an immediate rescore rather than waiting for the next scheduled cycle.
- Track trends, not just snapshots. A vendor sliding from 85 to 70 over two quarters tells a different story than one holding steady at 70.
- Preserve score lineage. Keep a record of what inputs and weights produced each historical score so an auditor can reconstruct any past decision.
Executive dashboards should show tier distribution and trend direction, not raw data dumps. Turning score movement into dollar exposure, using an approach like quantitative risk assessment, tends to land better with a board than a color-coded chart alone. Continuity-specific scoring tools, such as operational continuity assessment methods, help fill the resilience dimension with real inputs instead of guesswork.
Best Practices and Common Pitfalls
The biggest failure mode is letting one input dominate. A vendor with a great security rating and a terrible contract is still exposed; a vendor with a mediocre rating but airtight breach notification terms might be lower risk than the score suggests if ratings carry too much weight.
- Never let a single external rating override documentary evidence in a compliance decision.
- Document why each weight was set and tie it explicitly to engagement type.
- Apply conservative default scores to brand-new vendors with limited evidence history.
- Keep a human sign-off step wherever the outcome affects a regulatory filing or contract obligation.
Pro Tip: Build a one-page weight rationale document for every scoring policy update. When an auditor asks why financial stability carries 30 percent weight for a payment processor and 10 percent for a copywriting vendor, you want an answer on file, not a scramble.
Practical Implementation Notes From CisoSafe
A vCISO team calibrates scoring weights against the client's actual regulatory footprint rather than applying a generic template. A law firm with client trust account exposure gets different privacy and confidentiality weighting than an oil and gas operator managing SCADA vendor access.
- Weights get set during the initial risk assessment and reviewed at each policy cycle, not adjusted mid-review for individual vendors.
- Onboarding gates block go-live for vendors missing minimum evidence, with a tracked remediation workflow instead of an informal follow-up email.
- Refresh cadence follows tier: critical vendors on a quarterly cycle, with event-driven triggers layered on top for breach disclosures or certification lapses.
- Score lineage stays documented so leadership and auditors can trace exactly how a rating was reached.
vCISO Perspective: Balancing Automation and Human Oversight
Automation earns its keep on data collection and continuous monitoring. It should never make the final call on a vendor tied to a regulatory filing or a material contract term. Risk appetite, not technical capability, should decide where that line sits. A defensible score is one you can explain to an auditor a year later, not just one that produced a clean dashboard today.
— vCISO
How CisoSafe Helps Implement Defensible Third-Party Risk Scoring
This approach pairs hands-on vCISO strategy with an AI-enabled platform that automates evidence intake and produces board-ready reporting, offering an efficient alternative to building a scoring program from spreadsheets and generic templates.
For regulated SMBs and mid-market organizations in law, energy, and healthcare, that combination matters because the weighting and tiering decisions above carry real regulatory consequences. CisoSafe's vCISO and compliance program services cover scoring policy development, security risk assessments, and audit and certification readiness, mapped against frameworks like SOC 2, HIPAA, PCI DSS, and CMMC. Instead of a reviewer guessing at weights vendor by vendor, you get a documented policy, an automated intake process for questionnaires and certifications, and a vCISO who can defend the methodology in front of your board or an examiner. Visit the CisoSafe about page to see how the vCISO engagement model fits your compliance calendar, or reach out to scope a scoring policy review for your current vendor portfolio.
Sources
A questionnaire response is a claim, not evidence. Treat self-attestation as one input among several, and require documentary backing before it earns real weight in the score.
Security ratings give you a continuous signal about exposed infrastructure and public vulnerabilities, but they cannot see internal controls, employee training, or contract terms. Certifications close some of that gap, but only if you verify current status and scope rather than trusting a logo on a vendor's website. A SOC 2 report from two years ago covering a different business unit tells you almost nothing about today's risk.
- Vendor Risk Scoring: A Complete Guide in 2026
Structured vendor security questionnaires and a documented vendor cybersecurity assessment process make this validation step repeatable instead of ad hoc. Compliance artifact checklists, like this vendor compliance requirements checklist, can help standardize what documentation you actually collect.
FAQ
How Do You Assess Third-Party Risk?
You assess third-party risk by combining questionnaire responses, external security ratings, certification status, and financial signals into a weighted composite score, rather than relying on any single input. The Atlas Systems guide to vendor risk scoring recommends validating self-reported data against documentary evidence before it carries meaningful weight.
What Are the Levels of Risk Rating?
Most programs use three to five tiers, typically labeled something like low, moderate, high, and critical, each tied to a specific operational action such as standard monitoring, enhanced review, or onboarding freeze. The exact number and labels vary by organization, but the tiers should map directly to the score ranges your policy defines.
How Is a Risk Score Calculated?
A risk score is typically calculated using a weighted composite model that combines cyber, privacy, financial, and operational inputs, with weights set at the policy level based on engagement type. MetricStream's third-party risk approach emphasizes that these weights need to be documented in advance so the resulting score is reproducible and auditable.
What Does Third-Party Risk Mean?
Third-party risk refers to the exposure an organization takes on through vendors, suppliers, contractors, or other outside parties that touch its data, systems, or operations. It spans cybersecurity, privacy, financial stability, and operational continuity, and third-party risk scoring is how that exposure gets converted into a comparable, trackable number.
Does CisoSafe Help Build a Scoring Policy?
Yes. CisoSafe's vCISO engagements include scoring policy development, weight calibration by engagement type, and evidence intake automation as part of its compliance program management services. Pricing for these engagements is available on request through the CisoSafe team.