
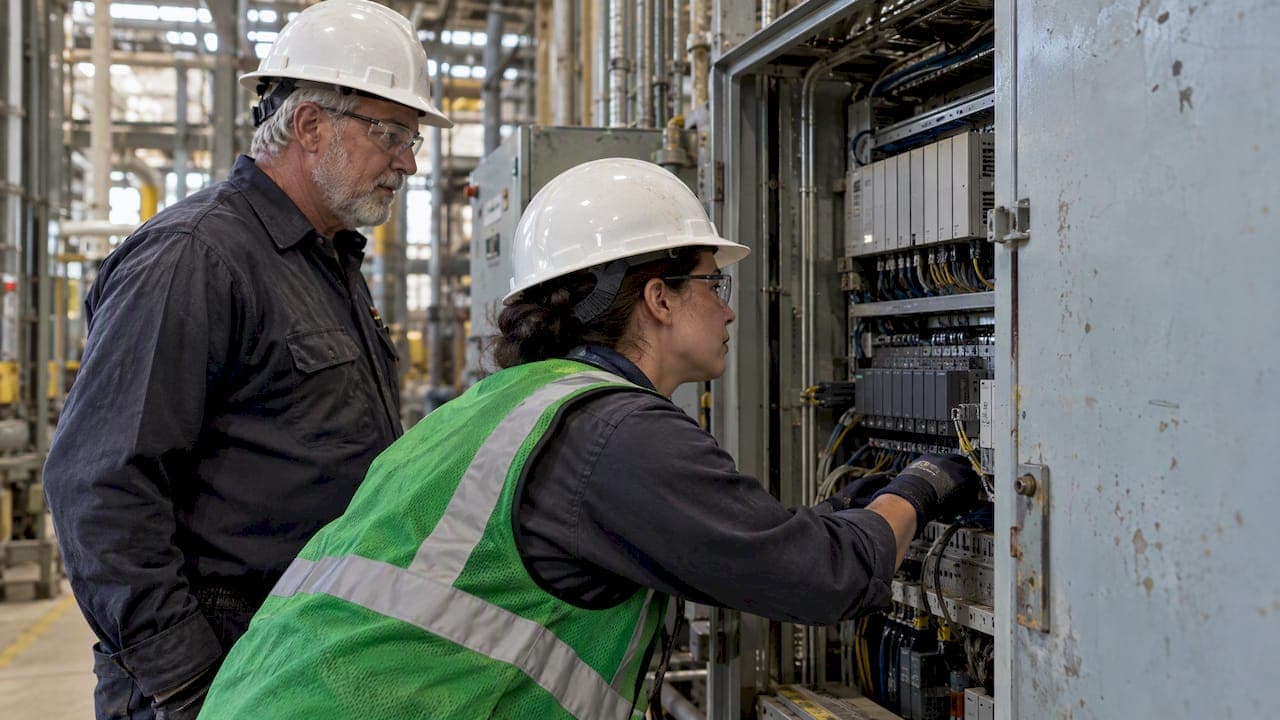
An OT asset inventory is a continuously maintained, taxonomy-backed record of OT systems, hardware, and software that enables prioritized vulnerability management, incident response, and operational continuity. It is built on short, structured data, not a one-time spreadsheet exercise. The first operational step is defining your scope and identifying the authoritative data sources (engineering diagrams, configuration backups, maintenance logs) you will reconcile against as the record grows.
TL;DR:
- An OT asset inventory must be continuously maintained, structured, and classified by function and importance to effectively prioritize remediation and response.
- Discovery methods include physical inspection, passive monitoring, configuration analysis, and active queries, with passive and physical methods being safest but less complete.
- Key inventory fields include asset number, role, IP address, criticality, and logs, which support risk management and operational decision-making.
- Regular updates should be tied to change-control processes, with documented provenance, review schedules, and lifecycle tagging to maintain accuracy over time.
- An effective inventory integrates with operational tools, supporting automation, dependency mapping, and audit reporting, ultimately becoming shared infrastructure rather than a static deliverable.
Table of Contents
- What makes an OT asset inventory different from an IT inventory
- Why an OT asset inventory matters beyond compliance
- Core fields and taxonomy models for an OT asset inventory
- How to discover OT assets without breaking production
- Keeping the inventory accurate: governance and lifecycle integration
- What to look for in an OT asset inventory platform
- A practical roadmap for building your OT asset inventory
- Practitioner guidance: common pitfalls and the KPIs that matter
- Inventory as living architecture, not a compliance deliverable
- How we help you operationalize your OT asset inventory
- FAQ
- Sources
What makes an OT asset inventory different from an IT inventory
An OT asset inventory is a regularly updated, structured list of operational technology systems, hardware, and software, paired with a taxonomy that classifies each asset by function and importance, according to CISA and partner agency guidance. That pairing matters: a list without classification tells you what exists but not what to protect first.
OT environments include programmable logic controllers, remote terminal units, human-machine interfaces, historians, engineering workstations, safety instrumented systems, and the network gear that connects them. Many of these devices run proprietary firmware, communicate over industrial protocols like Modbus or DNP3, and were never designed to answer a network scan. We cover the broader context of these systems in our OT cybersecurity primer, which walks through the asset classes most regulated operators manage day to day.
The discovery risk is the core difference from IT. An aggressive port scan that barely registers on a corporate laptop can freeze a legacy PLC or trip a safety interlock. NIST frames this directly: OT security has to preserve performance, reliability, and safety alongside confidentiality and integrity, which means discovery and remediation require engineering participation rather than a security team acting alone.
That engineering coordination changes who owns the inventory. IT asset management usually sits with a single team running automated discovery tools against a relatively uniform network. OT inventory work requires input from control engineers who know which devices are safety-critical, which protocols are in use on a given segment, and when a maintenance window allows for closer inspection. Build the inventory around that collaboration from day one, and the taxonomy you create later will actually reflect how the plant operates, not just what a scanner happened to see.

Why an OT asset inventory matters beyond compliance
Leadership buy-in for an inventory project rarely comes from a cybersecurity argument alone. The stronger case combines security outcomes with the operational value engineers already care about.
On the security side, an accurate inventory lets you prioritize vulnerability remediation by asset criticality instead of patching in the order vendors publish advisories. It also shortens incident response: when you already know what a device is, what it talks to, and who owns it, you cut the time spent figuring that out while an incident is active. CISA ties inventory and taxonomy directly to risk identification, vulnerability management, and service continuity.
On the operations side, the same record pays off in ways that have nothing to do with a breach. An accurate ICS asset record helps engineers locate failed components, diagnose incidents faster, and plan maintenance around actual equipment lifecycles rather than guesswork, a benefit NIST and SANS commentary both point to when building the business case for leadership.
The inventory supports several distinct use cases at once:
- Vulnerability management: matching advisories to specific firmware versions and asset criticality tiers instead of blanket patching.
- Incident response: giving responders a ready reference for device roles, dependencies, and network segments during an active event.
- Maintenance and obsolescence planning: flagging end-of-life hardware and firmware before it becomes a forced, unplanned replacement.
- Third-party and compliance alignment: documenting vendor-maintained devices and supporting audit evidence for frameworks that require asset visibility.
We cover the vulnerability management angle in more depth in our piece on upstream oil and gas asset risk, where prioritization by criticality tier makes the difference between a manageable patch cycle and a backlog nobody trusts.
Core fields and taxonomy models for an OT asset inventory
CISA's guidance identifies a set of high-priority fields that every OT inventory record should carry, and each one answers a specific operational question.
- Asset number and hostname: gives every device a stable identifier that survives network changes.
- Role or type: distinguishes a controller from a historian from a network switch, which drives how you classify risk.
- IP address and protocols in use: tells responders and engineers how the device communicates and what traffic to expect.
- Criticality: flags which assets matter most to safety and continuity, directly shaping patch and response priority.
- Logging status: records whether the device produces usable security or operational logs at all.
CISA's guidance connects these fields to risk identification, vulnerability management, incident response, and service continuity as a single chain, not separate benefits, according to the CISA asset inventory guidance.
Beyond cyber risk, maintenance and reliability arguments often unlock the budget and engineering cooperation a security team needs to get the inventory project started in the first place.
A handful of add-on fields turn a bare-bones inventory into something engineers will actually use: MAC address, vendor and model, serial number, firmware version, assigned owner, and known dependencies on other systems. None of these require exotic tooling to collect. Most come straight off a nameplate, a configuration backup, or an engineering drawing.
Once the fields are defined, choose a taxonomy model that fits how your team already thinks about the environment. Criticality-based taxonomy sorts assets by the operational or safety consequence of failure. Function-based taxonomy groups by role (control, monitoring, network infrastructure). Zones and conduits, drawn from IEC 62443 and echoed in CISA's architecture guidance, group assets by security boundary and the data flows that cross it. Most mature programs end up combining all three: zones and conduits for network segmentation decisions, criticality for patch prioritization, and function for day-to-day engineering reference.
How to discover OT assets without breaking production
Discovery is where most inventory projects either succeed quietly or cause an incident. SANS framing, echoed in recent industry analysis of the CISA guidance, groups discovery into four categories, and each has a distinct risk profile.
- Physical inspection: walking the floor and reading nameplates, the slowest method but the only one that reliably finds air-gapped or isolated devices.
- Passive monitoring: listening to network traffic without injecting anything, generally the safest automated method but blind to devices that rarely communicate.
- Configuration analysis: pulling data from existing backups, engineering drawings, and maintenance logs, which costs nothing in production risk but depends on how current those records are.
- Active discovery: querying devices directly, which produces the richest data but can disrupt legacy equipment that was never built to handle unexpected requests.
Passive discovery is safer but incomplete. Mature programs combine passive telemetry with physical inspection, configuration records, maintenance logs, and carefully controlled active queries to close the gaps each method leaves behind, a pattern Cybersecurity Dive's analysis of the CISA guidance describes as the practical baseline for mature programs. The same source notes that active discovery needs engineering sign-off before it touches any segment with safety-critical equipment, since even a routine query can behave unpredictably on older firmware.
Pro Tip: Before running any active scan on an OT segment, confirm the maintenance window, get written engineering approval, and have a rollback plan for the specific devices in scope.
The reconciliation step is where the real accuracy gain happens. Reconciling passive telemetry against engineering diagrams, configuration backups, maintenance records, and vendor documentation catches the false negatives passive monitoring alone will miss and flags stale records before they mislead a response team, a practice outlined in the same industry analysis. Partners worth checking your taxonomy against include frameworks built for broader asset management programs; the ISMS Calculator's guidance on asset inventory and ISMS effectiveness is a useful cross-check if your organization also tracks ISO 27001 alignment.
Keeping the inventory accurate: governance and lifecycle integration
A one-time inventory decays the moment it is finished. Operationalizing it means assigning clear ownership, wiring updates into existing workflows, and tracking the evidence behind every record.
Start with a named steward, usually someone with one foot in engineering and one in security, responsible for reviewing changes and resolving conflicting data. Without that role, updates drift to whoever happens to notice a discrepancy, and the record quietly goes stale.
- Tie updates to change control: any work order that adds, replaces, or reconfigures equipment should trigger an inventory update as a required step, not an afterthought.
- Record provenance: note where each data point came from (passive capture, physical inspection, vendor documentation) and when it was last verified.
- Set a review cadence: reconcile high-criticality zones more frequently than low-risk segments; a quarterly full review is a reasonable baseline for most regulated operators.
- Reflect lifecycle stage: tag each asset as planned, commissioned, in service, end-of-life, or decommissioned, so the inventory shows not just what exists but where it sits in its usable life.
Lifecycle tagging deserves particular attention because it is the field most programs skip. An asset nearing end-of-life carries different risk than a newly commissioned one, and that distinction should show up in how you prioritize patching and replacement budgets, not just in a separate maintenance spreadsheet. Our guide to secure remote access for OT teams covers a related governance pattern: treating access changes, like inventory changes, as events that require documented approval and a paper trail auditors can follow.
What to look for in an OT asset inventory platform
Whether you build the inventory in a spreadsheet, a dedicated OT visibility tool, or a broader security platform, the same capabilities separate a usable system from a static document.
- Continuous change detection: the platform should surface new or modified devices automatically rather than waiting for the next manual survey.
- OT protocol fluency: native understanding of industrial protocols, not just generic network scanning, to correctly identify controllers and field devices.
- Topology and context: a view of how assets connect, not just a flat list, so dependencies are visible during an incident.
- Vulnerability and lifecycle context: linking each asset to known advisories and its position in its usable life.
- Provenance and audit exports: every field traceable to its source and timestamp, ready to hand to an auditor without reconstruction work.
- Role-based access and integration points: APIs or exports to your SIEM, CMDB, or ITSM platform so the inventory feeds the tools your teams already use daily.
Integration matters more than any single feature on its own. An inventory that only lives in one tool eventually diverges from the maintenance system, the ticketing queue, and the vulnerability scanner that all touch the same assets. Platforms built for operational intelligence in adjacent domains, like Opsphere's topology mapping for infrastructure teams, illustrate the same principle applied to IT infrastructure: unify the data flows instead of letting each tool keep its own partial view.
A practical roadmap for building your OT asset inventory
CISA's guidance describes the work as a five-step process. In practice, each step produces a concrete deliverable you can point to when leadership asks for progress.
- Define scope and governance. Name the steward, pick the pilot zone, and agree on success metrics (for example, percentage of assets with verified provenance) before touching a single device.
- Run a pilot discovery. Choose one critical zone, combine physical inspection with passive monitoring and configuration review, and collect the CISA high-priority fields for every asset found.
- Build the taxonomy and classification rules. Decide how criticality, function, and zone-and-conduit groupings will be assigned, and document the rule set so future reviewers apply it consistently.
- Integrate data sources and automate reconciliation. Connect the inventory to configuration backups, maintenance logs, and any scanning tools in use, and define the KPIs (reconciliation lag, coverage percentage) that will track ongoing health.
- Institutionalize lifecycle management. Fold inventory updates into standard change-control workflows and set a recurring review cadence so the record keeps pace with the plant rather than falling behind it.
The pilot zone matters more than it looks. Picking a single critical area first lets you work out approval gates, discovery tradeoffs, and taxonomy decisions on a manageable scale before scaling the same process plant-wide. Our overview of industrial cybersecurity assessment types walks through how a focused assessment can double as that pilot, giving you both inventory data and a readiness baseline from the same engagement.
Practitioner guidance: common pitfalls and the KPIs that matter
The most common failure we see is the spreadsheet mentality: a team builds a thorough inventory once, treats it as finished, and watches it go stale within months because no process ties updates to actual plant changes. The second most common failure is skipping provenance, so when two sources disagree on a device's firmware version, nobody can tell which one is current. The third is attempting active discovery without engineering sign-off, which risks the exact production disruption the inventory project was meant to prevent.
The mitigations are straightforward and worth stating plainly: pilot in a single critical zone before scaling, make change-control tickets the trigger for inventory updates rather than a separate manual task, and store evidence with reviewer notes so every field has a traceable source.

For leadership reporting, three KPIs tend to communicate program health better than a raw asset count: the percentage of assets with verified provenance, the average reconciliation lag between a plant change and its inventory update, and the mean time to reconcile a change on a high-criticality asset. Track those three, and the inventory starts speaking a language operations leaders already trust.
Inventory as living architecture, not a compliance deliverable
The biggest mistake we see in OT security programs is treating the asset inventory as a deliverable rather than infrastructure. A spreadsheet handed to an auditor once a year is not an inventory. It is a snapshot that was accurate on the day someone built it.
The real value shows up when engineering, security, and operations treat the record as shared architecture data: the same source maintenance teams check before a repair, the same source incident responders pull up during an outage, the same source compliance teams export for an audit. That shift changes who shows up to maintain it and how seriously the updates get taken.
Get those three functions aligned around one record, and the inventory stops being a project with a deadline. It becomes the thing the plant runs on.
— vCISO
How we help you operationalize your OT asset inventory
Building and maintaining an OT asset inventory to the standard CISA describes takes sustained effort: engineering coordination, careful discovery, governance that survives staff turnover, and evidence that holds up under audit. We provide services and compliance platform support designed to help teams achieve that outcome without adding a full-time hire.
If your team is short on internal capacity, facing an audit deadline, or needs board-ready reporting on where your OT assets stand today, that is exactly the gap our engagements close. Our approach combines advisory services to guide taxonomy decisions, governance structure, and pilot scope for your specific environment; compliance program management to tie inventory evidence to relevant frameworks; and a technology portal to centralize provenance, reconciliation status, and reporting in one place leadership can review.
We regularly work with regulated operators in energy, oil and gas, and other high-stakes industries requiring rigorous support without the cost of traditional consultancies or full in-house security teams. If you want a clear next step, visit our services overview to request an assessment and see where your current inventory stands against CISA's framework.
FAQ
Is a firewall IT or OT?
A firewall itself is an IT security device, but in OT environments it often sits at a zone boundary to enforce segmentation between IT and OT networks or between OT zones. Whether it counts as an "OT asset" in your inventory depends on your taxonomy, though most programs track OT-facing firewalls as network infrastructure within the inventory's scope.
What does OT equipment mean?
OT equipment refers to the hardware and systems that monitor or control physical processes, including programmable logic controllers, remote terminal units, human-machine interfaces, sensors, and safety instrumented systems. These differ from IT equipment because they directly affect physical operations, which is why CISA's guidance treats their discovery and management with safety-first constraints.
What is included in an asset inventory?
A complete OT asset inventory includes identifying fields like asset number, hostname, and IP address, operational fields like role, criticality, and protocols in use, and lifecycle fields like firmware version and owner. CISA's guidance lists these as high-priority fields because each one directly supports vulnerability management, incident response, and service continuity.
How often should an OT asset inventory be updated?
There is no single mandated interval, but CISA's guidance frames the inventory as something that must be regularly updated rather than built once. Most regulated operators tie updates to change-control events as they happen and run a full reconciliation review on a recurring cadence, often quarterly for high-criticality zones.
Is NIST SP 800-82 still the current OT security reference?
NIST SP 800-82 Revision 3, published in 2023, remains the finalized reference for OT security guidance as of this writing. A Revision 4 is available only as an initial public draft, so audit evidence should cite Revision 3 until Revision 4 is finalized.
Sources
- Foundations for OT Cybersecurity: Asset Inventory Guidance for Owners and Operators
- Cybersecurity Dive analysis of OT inventory guidance
- NIST SP 800-82 Revision 4 initial public draft